Securing Web Traffic with Automated HTTPS Enforcement
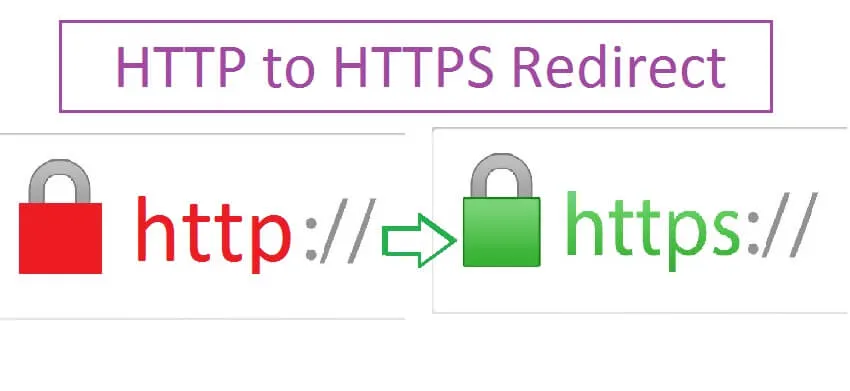
HTTPS is a confirmed Google ranking signal and an essential web security standard. Automatically redirecting all unencrypted HTTP traffic to HTTPS protects user data, prevents "Not Secure" browser warnings, and consolidates search engine ranking signals under a single canonical HTTPS protocol.
1. Apache / .htaccess Automatic HTTPS Redirect
Add the following rewrite rules to the top of your root .htaccess file to redirect all incoming HTTP traffic to HTTPS with a 301 Permanent Redirect:
RewriteEngine On
RewriteCond %{HTTPS} off
RewriteRule ^(.*)$ https://%{HTTP_HOST}%{REQUEST_URI} [L,R=301]
2. Nginx Server Block Configuration
For Nginx web servers, configure a dedicated HTTP server block that returns a 301 redirect to HTTPS:
server {
    listen 80;
    listen [::]:80;
    server_name yourdomain.com www.yourdomain.com;
    return 301 https://$host$request_uri;
}
3. Next.js App Router HTTPS Enforcement
In modern Next.js deployments, HTTPS is automatically enforced by edge platforms like Vercel or Cloudflare. To configure HSTS security headers in next.config.js:
module.exports = {
  async headers() {
    return [
      {
        source: '/(.*)',
        headers: [
          {
            key: 'Strict-Transport-Security',
            value: 'max-age=63072000; includeSubDomains; preload'
          }
        ]
      }
    ];
  }
};